

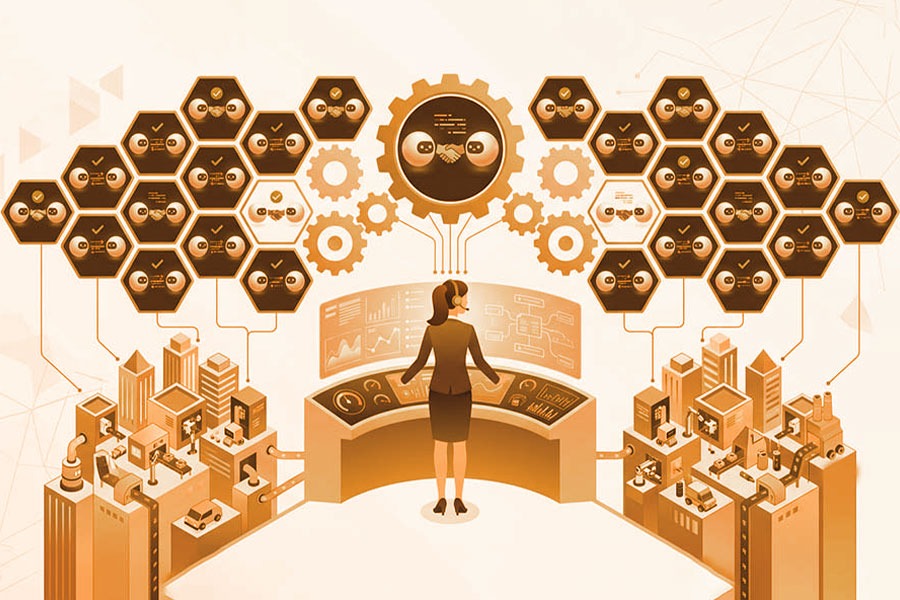
Enterprise operations are shifting from people orchestrating automation to environments where artificial intelligence (AI) agents can communicate, coordinate, negotiate and execute tasks across digital systems. Enterprise software has traditionally been used to help employees execute transactions, enforce pre-defined rules and automate repetitive tasks. Agentic AI enables software to interpret objectives, select the right tools, exchange information with other agents, and complete multistep workflows with limited human intervention.
This transition introduces machine-to-machine scale: an operational environment where software agents talk to each other across enterprise applications, vendors, business units, application programming interfaces (API), and external digital services. Organizations can use specialized agents to execute interrelated tasks instead of relying on employees to perform every single step. For example, a procurement agent could compare supplier offers, verify purchasing requirements, negotiate predefined commercial terms and coordinate with a finance agent to prepare an authorized transaction.
The Chief Information Officer (CIO) needs to take on responsibilities beyond managing infrastructure, applications and technology investments as these capabilities grow. CIOs will have to increasingly define the communication paths of autonomous agents, what decisions they can make, what resources they can access and when they need human approval.
The key question is one of operational independence versus enterprise control. “Organizations need to allow software agents to operate effectively without sacrificing security, accountability, regulatory compliance, or strategic objectives.” This calls for a governance framework wherein autonomy is balanced by transparent policies, verifiable identities, constant surveillance, and appropriate oversight by humans.
Also Read: CIO Influence Interview with Srinivasan Panchapakesan, Chief Platform Officer at Hexaware
Understanding the Scale of Machine-to-Machine in Enterprise Operations
Enterprise is the machine-to-machine scale. Software agents interact with other agents and digital systems to coordinate work across multiple processes. Instead of being stand-alone tools, these agents can be part of interconnected workflows involving data sharing, resource assignment, decision making and transaction processing.
For CIOs, the importance is in managing not just individual AI applications, but the relationships and dependencies created as autonomous systems begin to coordinate enterprise activities.
a) From System Integration to Agent-to-Agent Collaboration
In traditional enterprise integration, applications are linked together using APIs, predefined workflows and predefined business rules. These integrations enable systems to share information and trigger certain actions, but they typically need well-defined instructions and pre-existing process logic.
Collaborating Agent to agent collaboration is a more dynamic approach. Agents act independently, interpreting tasks, identifying relevant capabilities, requesting information, and coordinating actions as circumstances change.
For example, when inventory reaches below a certain thresholda supply chain agent could:
- Ask the supplier agents about availability and pricing.
- Compare delivery schedules, costs and contractual requirements.
- Check with an inventory planning agent to confirm demand.
- Generate a purchase order with a procurement agent.
- Notify the responsible employee if the proposed purchase is beyond the authorized budget.
This may require less manual coordination and increase responsiveness. But agents have to operate under common protocols, data standards and explicit permissions. Without those foundations, dynamic collaboration can generate conflicting instructions, duplicated transactions or unanticipated dependencies.
b) What Happens When Software Agents Negotiate?
Software agents can negotiate by exchanging information, evaluating alternatives and proposing action within predefined commercial or operational boundaries. They can compare prices, evaluate service level agreements, reserve resources or coordinate purchasing decisions, depending on their capabilities and permissions.
Take the case of a company that buys cloud computing capacity. For example, a purchasing agent may compare offers from several suppliers, a technical agent evaluates the performance requirements, and a finance agent checks the budget available. The agents can evaluate acceptable options and recommend or select a service that meets the organization’s needs.
Negotiation does not mean carte blanche or the power to make binding agreements. Companies need to separate activities that an agent can do on its own and activities that need human approval. CIOs need to set boundaries that encompass:-
- Maximum spending and acceptable price differences.
- Requirements on service level and acceptable contract terms.
- Approved suppliers, platforms and counter-parties.
- Conditions requiring legal, financial or management approval.
- Processing of bids above authorized limits.
Such safeguards allow agents to coordinate commercial activities without giving them unlimited authority to commit organizational resources.
c) The Difference Between Automated and Autonomous Execution
Classic automation works on the basis of pre-programmed instructions. For example, a robotic process automation workflow can extract invoice information, validate specified fields and route a document for approval. Its behavior is mostly determined by predefined rules and process settings.
Agentic systems can operate in various ways. They can understand a goal, decompose it into subtasks, choose among available tools, assess intermediate results, and revise their strategy when circumstances change.
This distinction matters because autonomous execution offers more flexibility, but also more uncertainty. Even if the individual tools do what they are supposed to do, an agent can choose a strange sequence of actions, misinterpret an instruction, or generate an inappropriate output.
Thus, CIOs need to govern not only what agents can see, but also what they can decide and do. Transaction limits, validation points, execution logs and escalation paths and limited tool access are key safeguards.
Autonomy should be given according to the possible consequences of an action. Routine, reversible tasks may require minimal or no intervention, whereas high-value transactions, changes to sensitive data and consequential contractual decisions may require explicit approval.
d) The Impact of Machine-to-Machine Scale on Enterprise Governance
Managing machine-to-machine operations is difficult because agents can operate at high speed, interact repeatedly and initiate actions across interconnected systems. A decision in a single workflow can have implications for procurement, finance, inventory, customer service, and external suppliers.
For example, an agent responding to a demand forecast could initiate a replenishment request that triggers the supplier confirmation, payment preparation, and logistics scheduling. If the original forecast is wrong, or if the agent misinterprets a purchasing policy, then the resulting actions may propagate through multiple systems before an employee catches the problem.
Traditional IT governance remains a necessity but must evolve to include autonomous interactions and their aggregate impact. CIOs should concentrate on four priorities:
- Identity and Authorization: Verify the identity of each agent and limit its access to only the allowed resources and actions.
- Policy enforcement: Consistently enforce business rules, financial limits, and contractual constraints on agent interactions.
- Observability and accountability: Log decisions, communications, tool usage, and transaction results to facilitate investigation and auditing.
- Human supervision and recovery: Define escalation limits, emergency shutdown procedures and ways to reverse or compensate for wrong actions.
Governance must also extend to third-party agents working through vendors, SaaS platforms, and partner ecosystems. External agents may have different security practices, data handling policies and execution capabilities. Interoperability and trust are key concerns.
Finally, the magnitude of machine-to-machine shifts enterprise governance away from managing individual applications and toward managing a web of interacting digital decision-makers. CIOs need to create an environment where agents can collaborate effectively, but within very clear guidelines. The goal isn’t to eliminate humans from the loop but to automate execution that is safe, auditable and aligned with business priorities.
The New CIO Mandate: Managing the Autonomous Enterprise, Not Managing Technology
Machine-to-Machine operations are redefining the role of the Chief Information Officer (CIO). CIOs have historically focused on technology infrastructure, application integration, cybersecurity coordination, and digital transformation. CIOs also need to manage how digital systems decide, exert authority, and interact across organizational boundaries as AI agents start negotiating with other agents and performing enterprise workflows.
The shift involves moving from managing technology assets to governing autonomous enterprise behavior. CIOs need to ensure agents are operating within the parameters of business objectives and organizational policies, and are held responsible for their actions. The objective is not to centralize every decision, but to put in place coherent boundaries within which autonomous systems can operate safely and efficiently.
a) Governing Digital Decision Making
AI agents will be increasingly capable of understanding goals, evaluating options, and executing actions without human approval at each step. But some decisions cannot be made alone. Changing a vital production system is not the same as approving a big financial transaction or making a simple inventory adjustment.
CIOs should work with business leaders to determine what agents can do without approval and what they cannot. These boundaries must be consistent with financial exposure, operational impact, regulatory obligations and the reversibility of any action.
For example, an agent may identify a lack of software licenses on their own and then consider the purchasing options available. You may also be allowed to create a purchase order. You may need procurement or finance approval to commit to a big expense.
Good decision governance should establish:
- Permitted and forbidden actions for each agent.
- Transaction caps and spending limits.
- Cases that require human approval.
- Access restrictions to sensitive systems and information.
- Processes to pause execution if there is uncertainty or policy violations.
These controls enable autonomy without allowing agents to interpret business objectives as an unrestricted mandate.
b) Designing the Enterprise Agent Strategy
The enterprise agent strategy should tie AI capabilities to measurable business priorities, not just encourage organizations to deploy agents wherever automation looks possible. CIOs must identify workflows where autonomous orchestration can increase efficiency, accelerate processes, or improve the quality of decisions.
You can find starting points in areas like invoice processing, IT incident triage, comparing suppliers, retrieving internal knowledge, and handling routine service requests. These activities are often easier to evaluate because they have identifiable inputs, measurable outputs, and set rules.
Before deployment, CIOs should assess existing processes, data availability, integration requirements, and potential failure scenarios. They also need to figure out whether a workflow is better served by agentic reasoning or by traditional automation.
As part of the strategy, reusable agent capabilities, shared integration services, common identity systems, and standardized monitoring should be defined to align with enterprise architecture. That removes duplicated development and makes it easier to govern agents across departments.
A phased approach can be especially useful. Organizations can begin with supervised pilots, measure performance, correct operational deficiencies, and only when evidence indicates the system can meet reliability and governance requirements, grant further autonomy.
c) Establishing Enterprise-Wide Agent Policies
More agents means individual teams may take different approaches to permissions, monitoring, communication, and risk management. Without common standards, these differences can lead to security gaps and inconsistent operational behavior.
CIOs should adopt enterprise-wide policies covering the full agent lifecycle, including registration and authorization, deployment, monitoring, modification, and retirement. Key policy areas include:
- Identity: Each agent must have a verifiable identity and an accountable owner.
- Permissions: Use only the resources and actions needed to perform approved tasks.
- Communication: Agents must communicate via authorized interfaces and supported protocols.
- Execution: Financial, contractual, and operative activities must be kept within the established limits.
- Monitoring: Decisions, tool calls, exceptions, and results should be properly logged.
- Escalation: Agents must understand when to stop, ask for help, or transfer a task to an authorized employee.
Central governance does not mean central execution. Individual departments can build and run specialized agents while adhering to shared enterprise standards. This balance allows business units to innovate without creating disconnected systems of control.
d) CIO, CISO, CFO, and Business Leadership Coordination
The technology function cannot manage enterprise governance independently. It requires cross-collaboration across tech, cyber, finance, legal, procurement, compliance, and operational leadership.
The CIO is responsible for the architecture, integration, technology strategy, and governance mechanisms that support agent deployment. The Chief Information Security Officer (CISO) is concerned with identity, access, threat prevention, incident response, and system integrity. The CFO (Chief Financial Officer) helps to establish financial authority, transaction limits, and controls over economic exposure.
Legal and compliance teams can weigh in on issues of contractual obligations, regulatory requirements, and questions of accountability. Business leaders are checking whether an agent’s capabilities match operational goals and whether its performance is up to snuff.
And ownership is important. Each production agent should have a business owner and technical owner, with defined responsibilities for capability approval, incident review, and measurement of results.
Routine cross-functional reviews can evaluate agent performance, probe exceptions, and decide whether to increase or scale back autonomy. This shared model makes autonomous execution an enterprise governance responsibility, not a standalone technology experiment.
The Architecture of Machine-to-Machine Enterprise Operations
The architecture needs to interface autonomous agents with enterprise applications, communication protocols, identity services, policy engines, and monitoring systems to enable machine-to-machine enterprise operations. They allow agents to share information and to do work, while keeping the organization in control.
a) Agentic Architecture and MAS
Multi-agent architectures decompose complex workflows into specialized agents. One agent might interpret a request, another might research options, a third might validate policies, and a fourth might execute an approved action.
Think of a procurement process where a sourcing agent checks suppliers, a compliance agent checks vendor requirements, and a finance agent checks for budget availability. There is an orchestration layer that coordinates all of their activities and makes sure that each task gets whatever info it needs before it moves on.
Orchestration matters because agents may give conflicting recommendations, have incomplete data, or attempt to do things in the wrong order. Rules about managing dependencies, who owns tasks, deadlines, and how to resolve conflicts help keep things consistent.
CIOs also need to determine when agents should talk directly to each other and when all communication should flow through a centralized orchestrator. Direct communication brings flexibility; orchestration offers better visibility and control for complex workflows.
b) Large language models and AI agents
Large language models allow agents to interpret instructions given in natural language, to put together information, to generate plans, and to choose appropriate tools. An agent can thus leverage these capabilities to decompose a high-level goal into smaller tasks and change its strategy when intermediate results do not match expectations.
But language models should not decide every operational rule by themselves. Activities such as financial calculations, permission checks, transaction validation, etc., that require precision often require deterministic software and known business logic.
A well-designed architecture combines reasoning with language models, structured rules, databases, conventional software, and validated decision systems. The model could recommend an action. And then you could have a separate policy service that says if that action is permitted.
This separation reduces the risk of generated text being treated as authorization, and helps make execution more predictable.
c) M2M communication and interoperability
Different vendors or departments may develop agents with different data formats, different ways to communicate, and different ways to describe capabilities. Interoperability allows them to share requests, discover available services, communicate task status, and consistently interpret execution results.
Common templates and written procedures let agents know what information is required and what kind of responses they are likely to receive. Communication standards can also reduce reliance on a single platform.
Before linking agents across organizational boundaries, CIOs should assess protocol compatibility, message validation, error handling and version management. External communications should be protected from malicious instructions, unauthorized data disclosure, and unverified counterparties.
d) Enterprise Applications, APIs, and Access to Tool
Agents typically interact with enterprise systems via application programming interfaces. These interfaces connect to ERP platforms, CRM applications, procurement systems, financial software, HR platforms, and IT service management tools. But just because you have access to an API doesn’t mean you get to do everything it can do.
CIO controls to put in place include:
- Read-only access for when changes aren’t required.
- Direct permission of sensitive operations.
- Transaction limits and input validation.
- Rate limits to avoid too many or repeated requests.
- Approval checkpoints for high-impact operations.
These controls allow agents to take advantage of enterprise tools while mitigating the impact of incorrect instructions or unexpected behavior.
e) Agent Authentication and Digital Identities
Each autonomous agent needs an identity that distinguishes it from other agents, human users, and external services. Without reliable identification, organizations cannot reliably enforce permissions or determine responsibility for machine-generated actions.
Enterprise identity systems must link agents to responsible owners, permitted purposes, authorized resources, and applicable operational environments. Authentication verifies the agent’s identity, and authorization specifies what the agent is allowed to do.
Delegated credentials should be narrowly scoped and time-limited when appropriate. Rotating credentials, revoking credentials, and logging activities reduce the risk of compromised credentials being used to access sensitive systems. Agent identity should be preserved across delegated tasks, allowing organizations to trace the origin of a request even when multiple agents are involved in its execution.
f) Policy Engines and Execution Guardrails
Policy engines check actions against enterprise rules before they are executed. They can impose purchase limits, contract restrictions, data access policies, and approval requirements.
For example, a supplier-negotiation agent may find a good offer, but the policy engine may reject it if the contract contains prohibited terms or if the contract exceeds the authorized commitment.
The guardrails should not depend on the agent’s own reasoning. This is important since an agent could misinterpret a rule or perform an action that is not in line with its instructions.
The System shall prevent execution when an action to be taken violates policy, provide an appropriate explanation, and escalate the request if appropriate. Authorized personnel should also have emergency controls to suspend agents or disable specific capabilities.
g) Agent Observability and Execution Tracing
Observability provides CIOs insight into agent activity across complex workflows. Monitoring should focus not just on whether a task succeeded, but on how the agent reached its result, what tools it used, and what else it impacted.
Logs can include instructions, tool calls, authorization checks and transaction results. Distributed tracing allows investigators to correlate events across agents and applications to reconstruct failures across multiple systems.
Useful monitoring indicators are:
- Task completion/failure rate.
- Violations of policy and escalation of approval.
- Repeated execution attempts and duplicate transactions.
- Latency, infrastructure utilization, and operational cost.
- Unusual communication patterns and attempts to gain unauthorized access.
Observability should be coupled with alerting, incident response procedures, and clear ownership. If there is no one tasked with investigating major anomalies, you can’t just record an event and be done with it.
Managing Autonomous Agent Interactions for CIOs
Governance must extend from individual applications to the interactions between agents, as agents can negotiate and execute work across enterprise boundaries. CIOs need means of controlling levels of autonomy, defining negotiation authority, limiting delegated permissions, stopping conflicting actions, and maintaining human accountability.
a) Specifying Degrees of Agent Autonomy
Different agents require different levels of independence. CIOs can establish levels of graduated autonomy based on risk and operational maturity.
The practical model is given as:
- Agents seek, organize, and synthesize approved information.
- Agents should explore options and present them to the employee for a decision.
- Agents prepare or execute actions that require approval.
- Agents autonomously execute predetermined actions within narrow boundaries.
The level should be determined by financial exposure, reversibility, data sensitivity, and potential impact on customers or operations. Only after performance in the real world has been confirmed should organizations increase autonomy.
b) Establishing Negotiation Boundaries
Negotiation agents need clear boundaries for the terms they can offer, accept, or reject. These limits can be pricing, discounts, delivery schedules, service levels, and suppliers’ resource allocation. A procurement agent could negotiate within an approved price range but might escalate if a supplier asked for a longer contractual commitment or presented unfamiliar terms.
Negotiation policies should define acceptable outcomes, unacceptable conditions, and triggers for escalation. Agents should also make a distinction between recommending an agreement and legally binding the organization to the agreement.
c) Authorizations and Delegated Authority for Managing Agents
Agents may have to delegate subtasks to other agents, but this cannot be used to circumvent access restrictions. Permissions should be limited by task, resource, duration, and operation allowed. A research agent may pull supplier data without the authority to place orders, and a purchasing agent may draft transactions without full access to financial institutions.
Delegated agents should only inherit the permissions necessary to do the work they are assigned. Authorization checks should be enforced throughout the workflow and not just at the start of the first task.
d) Avoiding Conflicting Decisions and Loops in Execution
Connected agents may inadvertently produce duplicate transactions, issue conflicting orders, or repeatedly trigger each other. When execution outpaces human review, such failures become more consequential.
CIOs should establish unique transaction identifiers, idempotency controls, execution limits, and conflict-resolution mechanisms. Idempotency helps avoid unintentional duplication of operations with repeated requests.
Systems should also detect multiple agent-to-agent triggers and impose limits on retries, delegation depth, and workflow length. If conflicts can not be resolved safely, execution should be suspended for review.
e) Human Approval and Escalation Mechanisms
Human supervision is still required when an action exceeds an agent’s authority, involves significant uncertainty, or could have large financial, legal, security, or operational consequences.
Agents must be configured to stop and escalate when they come across conflicting records, unknown contract terms, suspicious activity, or requests beyond approved policies.
A good escalation should give the reviewer the suggested action, backup information, policy limitations and possible outcomes. This way, employees can make informed decisions and not just approve a recommendation that they don’t understand.
The goal is to make human intervention selective and meaningful. The routine activities can be done within the set limits, and the high-impact decisions are still subject to appropriate review. In this paradigm, CIOs allow machines to collaborate while maintaining the authority of the enterprise (and therefore the security, observability, and organizational purpose) of autonomous systems.
Machine-to-Machine Agent Governance for Business Applications
The future of enterprise operations could well lie in machine-to-machine agent governance, with software agents orchestrating activities across business functions, applications, and external service providers. Rather than having employees engaged in each interaction, organizations may employ specialized agents to communicate, assess options, and execute tasks on their behalf.
But autonomous execution should still be tied to measurable objectives, security requirements, and business policies. CIOs must make sure that agents can work together effectively without creating uncontrolled financial commitments, operational disruptions, or compliance risks.
a) Procurement and negotiation with independent suppliers
In the area of governance, one promising application is procurement. Purchasing workflows have well-defined approval processes, structured requirements and repeated comparisons. Before offers are identified as suitable, supplier-facing agents can assess pricing, product availability, delivery schedules and service level agreements.
For instance, the procurement agent may request quotes from approved suppliers and then evaluate them based on the purchasing needs and negotiate pre-defined commercial terms. It could then work with a finance agent to see if the budget is available, and an inventory agent to confirm demand.
Governance mechanisms need to define clear boundaries of authority to purchase. They are:
- Price bands and expenditure limits.
- The criteria for contract eligibility and supplier vetting.
- Procedures for evaluation of service commitments and delivery terms.
- Requirements to approve unusual agreements or high-value purchases.
Agents have the authority to create purchase orders on their own, but any legally binding contracts must align with the organization’s authorization policies.
b) Finance and Coordination of Autonomous Transactions
Financial operations consist of a number of interrelated activities such as invoice processing, payment preparation, account reconciliation, and cash-flow monitoring. Agents can collaborate on these workflows by sharing information across enterprise resource planning systems, banking platforms, and accounting applications.
For example, an invoice processing agent might compare a purchase order and a delivery confirmation to an invoice. If the transaction meets the specified criteria and the records are consistent, the system may ready the payment for execution by the authorized party. If reconciliation does not work, finance agents can also identify odd transactions, find inconsistencies, and notify appropriate employees.
We need strong controls. Organizations should establish a clear separation of duties between the preparation, approval, and execution of transactions. Payment limits, fraud detection, duplicate payment checks, and audit trails help to avoid errors and unauthorized transfers. The agent’s assessment should not be the sole determinant for high-risk transactions; additional verification should be necessary.
c) Revenue and Sales Activities
Agents working on lead qualification, customer relationship management (CRM) updates, proposal preparation, and commercial negotiations can benefit sales operations.
A sales agent might assess an incoming lead, check relevant customer information and collaborate with pricing and inventory agents to generate an offer. It can negotiate within the approved ranges of d******* and be assured that the terms proposed are in conformity with the policies of the organization.
This method can help to ease administrative bottlenecks and allow sales teams to respond to customer queries faster.
CIOs need to put controls in place to manage contractual obligations, customer data, discounts and pricing. Agents must not bind the organization by unauthorized concessions, promise products not available or change terms of contracts outside their authority. Escalate high value agreements and unusual customer requirements to the right people.
d) Self-healing IT and infrastructure operations
In IT Operations, agents can monitor the infrastructure, troubleshoot an event, diagnose system errors, and perform authorized remediation actions. The use of multiple agents working together across cloud environments, service management tools, and monitoring platforms could result in more effective service restoration.
For instance, if an agent observes a rise in application latency, it can query monitoring agents to obtain diagnostic information, detect a possible resource shortage, and recommend acquiring additional computing power.
It can automatically distribute resources where policies allow. However, they may require human approval for changes impacting critical applications, security settings or production databases.
CIOs need to implement such safeguards as emergency shutdown mechanisms, change management requirements, rollback procedures, and limited execution permissions. Agents also need to distinguish between symptoms and root causes that have been verified before they take potentially disruptive actions.
e) Synchronization of Logistics and Supply Chain
Supply chain success depends on the continuous coordination of inventory systems, manufacturers, suppliers, warehouses, and transportation providers. Agents can share availability information, modify replenishment requests, coordinate shipments, and react to disruptions.
One of the inventory agents might detect a shortage and then call the supplier agents to get updated delivery estimates. A finance agent might look at the cost implications, and a logistics agent might look at the transport options available.
These interactions enable organizations to respond to changes in demand and supply conditions without requiring employees to coordinate each transaction individually.
Governance should consider delivery deadlines, inventory levels, supplier reliability, transportation costs, and contractual obligations. Agents should also have contingency plans for unexpected logistics disruptions, conflicting inventory records, and unavailable suppliers.
f) Customer Service and Cross-System Resolution
Customer service agents can collaborate across billing, order management, CRM and support systems to resolve requests that would otherwise require multiple employees or departments.
For example, an agent responsible for a delayed order might pull up shipment information, check payment status, review the customer’s previous correspondence, and coordinate with logistics systems to provide an updated response.
This improves continuity across service channels and minimizes the number of repeated information requests. But, we have to keep checking to see who our customers are and limit their access. Agents should only retrieve the information necessary to respond to a request. Sensitive complaints, disputed transactions, refunds, and account changes may require us to verify you or get a human being involved.
g) Cybersecurity and Threat Response Autonomous
During cybersecurity operations, agents are deployed to help with incident response across security platforms, investigate alerts, analyze suspicious activity, and correlate threat intelligence.
If a possible compromise is identified, one agent might check the activity on the endpoint, and another agent might check the authentication logs. A coordinating agent could compile their findings and recommend containment strategies.
Threats that are verified may result in authorized agents quarantining affected endpoints or revoking compromised credentials. However, such actions can potentially interfere with legitimate business operations if the detection is inaccurate.
CIOs and security leaders need to lay the groundwork for when automated containment will be allowed and when human approval will be required. Agents also need protections against compromised identities, malicious instructions, and manipulated threat intelligence. You should be able to find out the evidence, authorization, and outcome of each consequential action.
Security, Trust and Accountability in Agent-to-Agent Enterprises
When software agents start to interoperate across enterprise boundaries, trust becomes an operational necessity rather than an abstract principle. Every interaction has potential risks in terms of the reliability of the information exchanged between systems, the authority of execution, access to data, and identity.
a) Impersonation and Spoofing of the Agent’s Identity
Attackers may also attempt to impersonate legitimate agents, compromise service identities, or use stolen credentials to gain access to enterprise systems. An unauthorized agent might be able to access confidential information or perform forbidden actions if the agent is considered trustworthy.
Organizations should verify agents and assign them verifiable identities before granting access. The authorization should be verified on an ongoing basis, especially when agents are requesting sensitive resources or delegating work.
Monitoring, fast revocation, credential rotation, and short-lived access tokens minimize the risk of compromised identities. Also, delegated permissions should be limited so that one agent does not delegate too much authority to another.
b) Prompt Injection and Malicious Agent Instructions
External documents, messages from suppliers, websites, or communications from compromised agents may contain malicious instructions for AI agents. These instructions might be intended to lead an agent in an undesired direction, reveal confidential data, or cause the agent to use a tool in an unauthorized way.
CIOs need to ensure that agents can distinguish between authorized instruction and untrusted content. Structured workflows, input validation, limited tool permissions, and independent policy checks mitigate the effect of manipulated information. Agents should never treat a message from another agent as a standing order to take a sensitive action. Trusted enterprise policies must validate critical operations.
c) Data Exfiltration Between Agent-Networks
Agents frequently share contextual information to achieve tasks, which may result in the inadvertent release of sensitive data. A procurement agent might want supplier pricing but has no good reason to release unrelated employee records or customer financial information.
The risks are mitigated by the use of information classification and data minimization. The control of access should specify what data each agent is allowed to read, process, and send.
Organizations should also develop policies for handling sensitive information across external services, use appropriate encryption, and monitor outbound information flows. The objective is to give agents sufficient context to do their jobs without exposing data that is not relevant.
d) Liability for Autonomous Acts
Autonomous execution should not create any ambiguity about who is responsible for a decision. Organizations need to know who (person or team) deployed the agent, what policies were applied, what instructions were provided to the agent, and which agent performed an action.
Audit logs should record relevant inputs, tool invocation, approvals, policy checks, and results of transactions. These logs can support investigations if an agent steps outside an accepted boundary or makes a wrong decision.
“Accountability has to be built in before you deploy.” The technical and security teams are responsible for the systems and controls that enable safe execution, while business owners are responsible for the intended outcomes.
e) Failure Recovery and Reliability Incident Management
Agents can be faced with incomplete information, loss of connectivity, request repetition or executing only part of a workflow. When systems are joined together, one failure can have a major ripple effect on a large number of downstream systems.
Organizations should implement retry limits, transaction validation, duplicate request protection, and circuit breakers to prevent the spread of repeated failures. Rollback procedures or compensating transactions can be used to get back to an acceptable state.
Incident-response plans should include instructions on how to pause, isolate or disable agents. Furthermore, recovery processes should find out whether partially completed actions need to be corrected before the workflow can proceed.
f) Third party agent and vendor-related risks
External actors using supplier platforms, software as a service applications and partner ecosystems may have different ways of handling data and security controls.
CIOs should evaluate vendors’ security capabilities, identity management, data retention, incident reporting, and audit provisions before allowing cross-platform interactions. Contracts should contain obligations on data exposure, service interruptions, and unauthorized acts. Third-party agent access should be restricted to pre-approved purposes. Given the sensitive and potentially impactful nature of their activities, their activities should be monitored.
Assessing the Effectiveness of a Machine-to-Machine Business Enterprise
The evaluation of machine-to-machine operations should be based on tangible business results, not on the number of agents deployed or tasks automated. CIOs are looking for performance indicators that show how much autonomy improves governance, reliability, financial results, and efficiency.
a) Completion of Workflow and Operational Efficiency
Organizations should measure time to complete workflows, success rate of execution, manual intervention, processing delays, and exceptions not handled.
By comparing these indicators to pre-deployment baselines, it is possible to determine whether agents are reducing operational friction or simply shifting work to other teams. The value of expedited execution is dependent upon the continued presence of acceptable quality and control.
b) Negotiated Results and Financial Performance
Financial indicators may include cost of rectifying agent errors, utilization of resources, pricing compliance, transaction-processing cost and realized procurement savings.
Negotiation performance should be measured against approved commercial objectives, not just headline discounts. A lower purchase price is not necessarily a real saving if it is accompanied by bad contractual terms or higher costs of delivery.
c) Quality and Reliability of Decisions
Reliability metrics track successful transactions, execution errors, duplicate operations, policy violations, and recovery time. Decision quality can be assessed by comparing agent recommendations to verified outcomes and expert assessments.
Organizations should also monitor the performance of the agents under several operating conditions to identify the cases at which they become less reliable.
d) Security and governance measures
Governance indicators include unauthorized access attempts, audit completeness, policy exceptions, security incidents, and approval escalations.
These measures serve to identify deficiencies in monitoring, execution, and permissions controls. An escalation increase may indicate that the agent requires more context, policies are too tight, or a workflow should be redesigned.
e) Cost of the Agent and Return on Investment
Model use, infrastructure, integrations, security controls, maintenance, and human supervision are all part of the total cost of agent operations. These costs need to be offset against real benefits such as better use of resources, shorter processing times and reduced operational errors.
CIOs should regularly review performance and change deployments if costs exceed the expected benefits. If agents don’t prove they deliver consistent value, they may need to be redesigned, restricted or retired.
Ultimately, the success of machine-to-machine governance will come down to whether autonomous systems can deliver real benefits without compromising operational stability, security or accountability. With clear performance measures, ongoing evaluation, enforceable controls, and carefully chosen use cases, CIOs can scale agent-driven operations and retain enterprise trust and control.
Implementation Roadmap: Creating a Governed Agentic Enterprise
Creating a governed agentic enterprise is more than just deploying AI agents and connecting them to business applications. CIOs must set up the technical infrastructure, operational policies, security controls, and accountability mechanisms that allow agents to collaborate safely. The phased approach to implementation enables organizations to verify capabilities, uncover risks, and expand autonomy based on tangible results rather than assumptions.
a) Identify High-Value, Low-Risk Use Cases
The first step is to identify workflows where collaboration between agents can deliver measurable benefits without adding unacceptable operational risk. CIOs should be concentrating on the repetitive, well-defined activities that have clear inputs, predictable outcomes, and established business rules.
These are invoice validation, internal IT support, collecting information about the suppliers, inventory monitoring, and document classification. These workflows offer opportunities to test agent coordination without immediately turning over high-impact decisions.
For each proposed use case, there are various criteria to be evaluated.
- Business value, such as anticipated time savings and reduced operating costs.
- Data readiness, i.e., availability and quality of relevant data.
- Technical feasibility, such as application integration and system compatibility.
- Risk exposure, including financial, regulatory, security, and customer impacts
- Whether an erroneous action can be reversed, and if so, whether it can be safely reversed.
CIOs should establish baseline performance measures before implementation. This allows agent-assisted operations to be compared to existing processes to determine whether the technology offers meaningful improvements.
b) Establish Agent Inventory and Governance Standards
With more deployments, enterprises need a central inventory of their software agents. Without a reliable registry, organizations may not know what agents are running, what permissions they have, and what business processes rely on them.
An agent registry should include agent identity, owner, purpose, capabilities, authorized tools, dependencies, deployment environment, and risk classification. It must also document the models and external services used by the agent.
Governance standards should specify the approval, testing, deployment, updating, suspension, and retirement of agents. Changes to an agent’s capabilities or permissions should trigger a suitable reassessment, not be treated as a routine software update.
This inventory also helps identify duplicate capabilities across departments. Organizations can create reusable services, under an umbrella of common governance standards, instead of creating multiple agents that do similar things.
c) Build the Identity, Policy, and Observability Foundation
CIOs should implement basic controls for authentication, authorization, policy enforcement, and monitoring before granting agents authority to perform business transactions.
Each agent requires a verifiable identity and narrowly scoped permissions. Policy engines should validate proposed actions against business rules, spending limits, data access restrictions, and approval requirements. The sensitive operations should have some kind of independent validation, not just the agent’s reasoning itself.
Relevant decisions, tool invocations, inter-agent messages, authorization checks, and transaction results should be part of the observability infrastructure. Logs should be detailed enough to support investigations, but should not include unnecessary sensitive information.
Organizations should also have emergency controls that allow authorized personnel to suspend an agent, revoke its credentials, or disable a specific capability when suspicious behavior is detected.
It is important to establish these foundations early, as retrofitting governance after wide deployment can be costly and disruptive to operations.
d) Agent-to-agent Workflows Under Pilot Control
With the basic controls in place, organizations can experiment with multi-agent workflows in simulated environments or in tightly constrained production environments.
A procurement pilot could, for example, include supplier discovery, quotation comparison, budget validation and purchase-order preparation. The agents could suggest what to do but not actually do it at first. That would let the employees see what their options were before giving them more power.
Testing should include failure scenarios and normal operating conditions, including:
- Agents giving contradictory instructions.
- Applications not available or delayed responses.
- Repeated transactions and duplicate requests.
- Unauthorized activity and policy violation.
- Surprise supplier actions and false information.
Pilot assessments should include transaction accuracy, completion time, escalation frequency, recovery performance and user confidence. Additional autonomy is to be earned by showing that one is trustworthy and by having documented consent.
e) Scale Through Standardized Integration
Successful pilots can be scaled up using reusable APIs, common communication protocols, shared identity services, and standardized policy templates. This makes it easier to link new agents and helps to maintain consistent governance across business units.
CIOs need to be wary of siloed agent ecosystems that rely on proprietary integrations or data formats that don’t play well together. Instead, enterprise architecture should enable modular components that interact through documented interfaces.
Scaling also means capacity planning. As agent interactions increase, organizations should understand their infrastructure requirements, estimate costs, API quotas, monitor workloads, and bottlenecks. Adopting a common integration strategy makes it easier to add new capabilities, while maintaining control over the systems and data involved.
f) Audit and Continuous Improvement
Governance needs to be provided during the operational lifetime of an agent. Changes in business requirements, models, data sources, and external services can affect agent behavior even if the surrounding workflow does not change.
CIOs should create periodic reviews with metrics for performance, security incidents, policy exceptions, audit findings, and employee feedback. These reviews can reveal opportunities for improving instructions, permissions, data quality, or constraining unsafe capabilities.
Organizations should also evaluate agents when there are major model updates or changes to connected applications. If performance degrades, agents may need to be run in a supervised mode until the issue is corrected. It maintains the autonomy earned by evidence, rather than being bestowed once and for all after an initial successful deployment. Constant improvement.
CIO Leadership: From Connected Systems to Governed Machine Economies
As agentic AI matures, enterprises may morph into networks of interconnected software agents coordinating activities across departments, suppliers, customers, and digital marketplaces. This change could alter the way that organizations buy and sell services, negotiate, and conduct transactions.
The CIO will take on a growing role in shaping the technical and governance infrastructure that enables these interactions to run securely, reliably, and in line with enterprise objectives.
a) Enterprises as Networks of Negotiating Agents
In the future, the enterprise environment may be populated by specialized agents that handle procurement, finance, logistics, sales, and infrastructure management. These agents could dynamically coordinate tasks, exchange operational information, and negotiate within predefined boundaries.
For example, a demand planning agent might spot a looming inventory shortfall, a procurement agent might evaluate supplier options, and a logistics agent might compare delivery timelines. A finance agent could verify the financial impact before an authorized order is executed.
Such coordination could reduce delays between departments and help enterprises respond more rapidly to changing conditions. But it also would raise the stakes for dependency management, shared policies, and cross-system observability.
CIOs will have to manage agent-to-agent relationships, rather than just their individual capabilities.
b) Agent-to-Agent Commerce and E-Markets
Digital marketplaces will most likely play an increasing role to enable interactions where authorized agents can find services, compare offers, exchange requirements, and initiate transactions on behalf of the business.
The purchasing agent of a company could compare different providers of cloud services with performance needs, contractual terms and monetary limits. It could then make a recommendation or start a purchase approved by the relevant marketplace.
Enterprises will need to have verified counterparties, machine-readable commercial terms, transparent pricing, and mechanisms to confirm commitments for these interactions to be reliable.
Agents have to distinguish between a technically correct offer and a commercially or legally acceptable settlement. Major contractual commitments, unusual provisions and decisions with significant long-term impact may still require human approval.
c) Dynamic Enforcement of Enterprise Policies
Governance policies have traditionally been enforced through static rules and periodic reviews. In the future, decision policy systems may more and more evaluate decisions in relation to changing operational conditions, risk levels, and regulatory requirements.
For example, an organization may permit an agent to approve routine purchases independently during normal circumstances but require an additional authorization when expenditure increases dramatically or when a supplier exhibits unusual risk indicators.
Dynamic enforcement would enable enterprises to customize levels of autonomy according to context and not apply the same restrictions universally.
But changes in policy need to be transparent, tested, and auditable. If agents believe something is good for them, they shouldn’t be able to override their restrictions or approval requirements. Independent policy services and transparent escalation procedures will continue to be critical.
d) Ecosystems of Interoperable Agents
The success of agent-driven operations will partially depend on whether agents of different vendors and platforms will be able to communicate reliably. Shared protocols, common capability descriptions, compatible data formats, and trusted identity mechanisms can reduce barriers to integration.
Consistent approaches to authorization, error handling, transaction status, and accountability will be needed for interoperability. An agent must not only know how to communicate with another system, but also what the receiving agent can do.
CIOs should favor architectures that allow for modular integration and avoid unnecessary dependence on a single vendor. However, cross-platform communication must not violate security boundaries or expose confidential enterprise information.
e) The CIO as the architect of machine governance
The CIO’s future role will blend enterprise architecture, AI governance, cybersecurity, operational strategy and organizational accountability. CIOs will help define how autonomous systems will be engaged in business decisions and getting work done, rather than just deploying technology.
That includes establishing acceptable levels of autonomy, ensuring agents are observable, coordinating governance across departments, and measuring whether machine-to-machine operations deliver business value.
CIOs will also need to work closely with legal, finance, security and business leaders to ensure autonomous systems stay in line with company commitments and regulatory obligations.
It is not to take human judgment out of enterprise operations. The goal is to create a setting in which machines can autonomously execute appropriate tasks while people maintain meaningful control over decisions of substantial consequence.
Final Thoughts
The scale of machine-to-machine is a major change in enterprise technology, that turns software agents from isolated productivity tools into participants in interconnected business operations. Such agents can talk to each other and share information, negotiate within specified limits, coordinate work flow and execute authorized tasks across application and organizational boundaries. As these capabilities mature, the CIO’s role shifts from managing technology infrastructure to governing the digital environment in which autonomous systems operate.
This change requires a coordinated approach to architecture, identity, permissions, security, and accountability. Interoperable communication, governed access to enterprise applications, enforceable policy engines and full observability are needed for multi-agent systems. Organizations also need to build mechanisms to prevent conflicting actions, to identify compromised agents, to recover from failures, and to escalate decisions with consequences to qualified employees. These building blocks help ensure that more autonomy can deliver more operational complexity faster than it can deliver business value.
Well chosen use cases, measurable objectives and controlled pilots are the beginning of successful adoption. CIOs can scale autonomous capabilities based on evidence by building agent inventories, standardizing integrations and measuring performance against clear baselines. The readiness for wider deployment of an agent has to be evaluated against operational efficiency, financial outcomes, quality of decisions, security performance and total implementation costs. Both ongoing surveillance and periodic reassessment are important, since the behavior of agents, business requirements and external conditions change over time.
In the future, companies may increasingly act as networks of negotiating agents, coordinating procurement, finance, logistics, sales, infrastructure and external services. This means that interoperability and dynamic policy enforcement will become more and more important and the need of trusted identities and transparent execution records will be strengthened. Decisions that involve large financial commitments, sensitive information, contractual obligations and substantial operational risk will still need human supervision.
Ultimately, the future CIO will not be managing the systems employees use. The CIO will help design and govern the environment in which software agents interact, negotiate, and work. Success will not be measured by the number of autonomous agents deployed, but by the organization’s ability to deploy them in a secure, responsible, and effective manner, while remaining accountable to its business objectives.
Catch more CIO Insights: The Overlooked Security Risk Behind Enterprise AI Rollouts
[To share your insights with us, please write to psen@itechseries.com ]
